What Is Blockchain Tech? How Blocks and Ledgers Help Build Trust
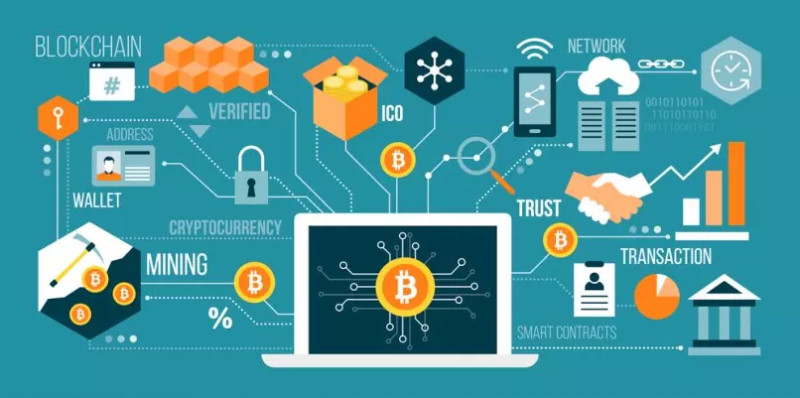
What Is Blockchain Tech
I've been getting questions about what is blockchain tech lately. People hear the word tossed around but don't always get a straight answer. So here's my take - no marketing fluff, just how it works under the hood.
Think of a blockchain as a shared digital ledger. Many computers keep copies of the same chain of blocks. That lets you check transactions without a central authority. It's the technology behind Bitcoin and other cryptocurrencies, but it can also help track who owns digital assets and where they come from.
How It Differs From a Traditional Ledger
A traditional ledger is a book or computer file that tracks economic activity - account balances, money movements, assets, contracts. Most conventional ledgers are maintained by a centralized organization like a bank. That bank stores records on its own servers and controls who can view or change them.
A blockchain distributes those records across nodes. Each node runs software, holds a copy of the ledger, and checks proposed changes. In the common public-chain model, participants don't submit additions to a single company's database. They submit transactions that are broadcast to a peer-to-peer network. Participants independently validate the transactions, package accepted ones into blocks, and reach agreement - consensus - about which version of the ledger is valid.
The term "distributed ledger technology," or DLT, is sometimes used as a synonym for blockchain. More precisely, DLT is the broader category, while a blockchain is one type of distributed ledger.
A blockchain specifically organizes data into linked blocks and commonly uses cryptographic linking, consensus, and incentives to agree on the ledger's state. This is where how do blockchain work becomes a practical question - it's not magic, it's a specific architecture.
The Basic Building Blocks
A blockchain system can be understood through a handful of components. Here's the mental model I use:
Core components
- Nodes - devices or computers that maintain a copy of the ledger and participate in the network
- Blocks - data structures that contain transactions or other records
- Transactions - records describing changes, transfers, or events
- Chain - the ordered connection linking one block to the previous block
- Validators - participants that check whether transactions and blocks follow the rules
- Miners - in PoW systems, the validators that perform mining work and compete to add blocks
- Consensus protocols - rules governing transaction validation, block creation, agreement, and synchronization
- Hash functions - functions that create fixed-length fingerprints used to detect changes and link blocks
- Public and private keys - cryptographic pairs used to authorize and verify transactions
- Digital signatures - values produced with private keys to demonstrate authorization
- Smart contracts - programmed instructions that execute or enforce conditions automatically
When someone asks what is blockchain software , I point to this stack. It's not one program - it's a set of protocols and data structures that work together.
Origins and Early Development
Protocols similar to blockchain were conceptualized as early as the 1980s and implemented during the 1990s for tasks like verifying document timestamps. The goal was to reduce friction and increase trust between parties that didn't know each other or shared no centralized institution.
In 1991, Stuart Haber and Scott Stornetta described a practical system for time-stamping digital documents. The aim was to make digital records difficult to backdate or alter. In 2004, Hal Finney introduced Reusable Proof of Work (RPoW), developing into digital cash and RSA-signed transferable tokens intended to address double spending.
Then 2008 happened. Satoshi Nakamoto published the Bitcoin whitepaper: "Bitcoin: A Peer to Peer Electronic Cash System." The proposed system added blocks to an original chain without requiring signatures from trusted parties. Bitcoin's open-source implementation launched in 2009. The word "blockchain" doesn't appear in the whitepaper - the term was popularized later by proponents of the technology.
The early classroom-style explanation of Bitcoin used a group of 30 children with virtual money. Their initial balances and transfers were first written on a chalkboard. A teacher could erase the board and assert control over the balances. The children therefore moved to separate notebooks, with each child keeping a copy of the transactions.
To avoid passing every individual note, the children exchanged pages containing batches of transactions. A new page included a sequence number and a hash of the preceding page. Recipients checked the page number, previous-page hash, transaction format, signatures, and account balances. Accepted pages were recorded in each participant's notebook. A numbered sequence of these pages represented a blockchain.
How Transactions Work - Keys, Signatures, Validation
A user account on a cryptocurrency blockchain is commonly represented by a public key or public address. The account also has an associated private key. The public key or address is like an email address - you can share it. The private key is like a password - its holder must keep it secret and use it to authorize spending.
In more precise cryptographic terms, the private key creates a digital signature that network participants can verify using the corresponding public key. A transaction generally includes the sender's address, the recipient's address, the amount or asset being transferred, and a digital signature. When the transaction is broadcast, nodes use the public key to check the signature and verify that the associated account has sufficient funds and that the transaction follows the network's rules.
The signature acts as cryptographic evidence that the holder of the private key authorized the transaction. It's intended to make an unauthorized change detectable. A person can also generate multiple public-private key pairs for separate purposes. If one key is compromised, another key system may remain unaffected.
Loss of a private key can make the associated assets inaccessible. Theft of a private key can allow another party to authorize spending. For that reason, decentralized systems often discuss backup keys, multisignature arrangements, key shards, social recovery, identity systems, and other mechanisms separate from the basic public-private key model. This is where how do blockchain works gets practical - key management is the user-facing part.
Hash Functions and Cryptographic Linking
A hash function converts data of any length into a fixed-length alphanumeric representation. A cryptographic hash is easy to calculate for a known input but designed to make it impractical to recover the input from the hash alone. The same input always produces the same output, while changing even one character generally produces a completely different hash.
A simplified example: assign numbers to letters (a=1, b=2, through z=26). The word "Hello" becomes 8 5 12 12 15. Multiplying those gives 86,400. If "Hello" were altered to "Hallo", the first letter becomes 1, producing 17,280. A recipient expecting 86,400 but receiving 17,280 could detect the change.
Real systems use much more complex algorithms like SHA-256. The values have little visible resemblance to the original letters because they're codes, not the original text. A hash by itself doesn't prove who sent a message - a separate digital signature provides that authentication. Cryptographic blockchains address these limitations by combining signatures, hashes, previous-block references, replication, and consensus.
Each block generally contains some or all of: data or transactions included in the block, the block's own cryptographic hash, the hash of the preceding block, a timestamp, a nonce or other consensus-specific value, and a header and metadata used for validation. The previous-block hash connects the blocks into a linear chain. Changing the data in an earlier block changes its hash. The next block then points to the old hash and no longer matches the altered block, making the discrepancy visible to other nodes.
Blocks and the Chain
Pending transactions are proposed to the network. Validators inspect each transaction, check signatures and account balances or state-transition rules, and collect valid transactions into a candidate block. A block may have a maximum amount of data or a limited number of transactions. Once it's accepted, it's appended to the chain and linked to the previous block.
The blocks create an ever-growing history. A simple structural analogy is a linked list where each data element contains a reference to the next element. In blockchain systems, the reference is cryptographic: each block's hash connects it to the preceding block. The last block in a conventional blockchain points to the previous block rather than the next one.
Each participant can inspect the same transaction history, subject to the network's access and privacy rules. Participants can independently verify or reject a proposed change. Redundant validation makes a unilateral alteration visible because one node's copy would differ from the copies held by other nodes.
Nodes are the computers participating in the network. A full node maintains a copy of the ledger and the rules needed to validate blocks. Some permissioned systems restrict which organizations may operate nodes or validators. Some public networks also distinguish full nodes from lighter wallet or verification services that don't maintain exactly the same amount of data.
Transaction Validation and Consensus
A generalized transaction lifecycle goes like this:
Transaction lifecycle
- A participant creates and signs a transaction with a private key
- The transaction is transmitted to the peer-to-peer network
- Nodes receive the transaction and independently check its format, signature, authorization, and available balance or state
- Validators or miners compete or otherwise participate under the network's consensus rules
- Accepted transactions are placed into a candidate block
- The block is linked to the previous block and given a cryptographic hash
- Other participants verify the block and the consensus result
- Once the block is sufficiently confirmed, the nodes update their copies of the ledger
- Additional blocks extend the chain and further reduce the possibility of reversing the transaction
In an idealized decentralized network, parties don't need to know or trust one another personally. They agree on a protocol and use the same validation rules. Every participant stores a copy of the result and can compare it with other participants. If one computer changes its copy, the altered copy won't match the agreed history.
This model reduces dependence on a "master copy." In a centralized database, a parent database may be treated as the single source of truth when replicas disagree. In a decentralized database, there's no single parent copy. The nodes communicate updates and reach consensus about the valid state.
Consensus can be understood as an agreed view of what the data contains and how it is labeled. Blockchain's distinguishing feature is not simply having copies. It is allowing independent participants to agree on updates without treating one organization's copy as the automatic authority.
Consensus mechanisms differ. Proof of work (PoW) has validators expend computing power to solve a network-specific problem - Bitcoin is the best-known example. Proof of stake (PoS) has validators secure the network based on stakes rather than mining with computational work. Proof of authority (PoA) uses recognized validators under an authority-based arrangement, commonly in private or permissioned blockchains.
PoW systems may reward the successful miner with newly minted cryptocurrency and transaction fees. The network's native asset can serve as an economic incentive for communication, validation, and consensus participation. This connects to explaining cryptocurrency - the token isn't just money, it's part of the security model.
Immutability, Finality, and Forking
Once a block has received enough independent confirmations, changing an earlier transaction would require creating a different version of that block and every later block. Other nodes would detect the conflict unless they also accepted the alternative history.
The cost of rewriting history increases with the number of subsequent blocks and the amount of independent validation or work protecting the chain. In PoW Bitcoin, an attacker would need more than half of the network's aggregate computing power to produce a competing history faster than the honest chain. A coordinated majority could theoretically produce a 51% attack by spending, censoring, or reversing recent transactions. The attack is described as impractical for a large, dispersed PoW network because of the computing equipment, electricity, and coordination required.
The longest-chain rule is sometimes used to resolve competing PoW histories: participants generally follow the chain showing the greatest accumulated proof of work. Immutable doesn't mean no correction can ever occur. A network may coordinate an upgrade, a hard fork, or another governance action. In such cases, participants choose which version to follow.
The 2016 classroom explanation emphasizes that once a page is changed with consent, every later page must also be changed. Participants who can't decide may trust the longest valid chain. Other blockchain work explicitly allows software upgrades, sometimes with waiting periods, advance notice, or constitutional limitations on emergency intervention. These descriptions differ in scope: ordinary confirmed records are difficult to edit, while protocol governance can still permit coordinated changes.
Public, Private, and Permissioned Blockchains
The earliest prominent blockchain networks were permissionless. Bitcoin, Ethereum, and Cardano are cited as decentralized networks whose computers are coordinated by consensus rules. But blockchain technology itself doesn't require permissionless operation. Private consortia and limited-membership networks can use blockchain structures.
Access models
- Public blockchain - permits open participation and uses independent validation
- Private blockchain - controlled by a restricted group
- Permissioned blockchain - allows open access under some conditions but limits participation to authorized members
- Consortium blockchain - governed by a group of organizations
Permissioned systems can be efficient because validators are known and rules can be administered more directly. However, their security and trust model depends on the integrity of the permitted validators and the administrator. If only a few participants can create blocks, those participants may input incorrect information or corrupt the system. A decentralized network attempts to reduce dependence on their trust by requiring a broader or cryptographically weighted group to agree.
Cryptocurrencies and Digital Money
Bitcoin demonstrates a public permissionless blockchain operating as a self-contained financial network. BTC is the native asset, and its issuance rules and hard cap are built into the protocol. The network has a stated maximum supply of 21 million BTC. Some advocates argue that this fixed and declining supply gives BTC properties they consider more resistant to inflation than currencies whose supply can be increased by a central authority.
Other cryptocurrencies may use public, private, consortium, or permissioned ledgers to record transfers. Ethereum and Cardano are cited alongside Bitcoin as decentralized networks. Tokens can represent a native digital currency, an asset, a voting right, access to an application, or another programmable set of rules.
Cryptocurrency can be purchased through wallets and trading platforms and then transferred digitally. The network records the transaction and the new owner. Public visibility, cryptography, timestamps, and transaction identifiers create an auditable record of payment. This is where people ask what actually is cryptocurrency or what is crypto exactly - it's a native asset of a blockchain network, secured by the same consensus that secures the ledger.
A 2021 market snapshot reported approximately 6,700 cryptocurrencies with a combined market value of about $1.6 trillion, with Bitcoin accounting for most of the value. At that time, one BTC was reported as worth about $60,000.
Volatility is real. Bitcoin had been approximately $450 in 2016, rose to about $16,000 in 2018, fell to around $3,100, and later increased above $60,000. Speculation can create major gains for some buyers while causing large losses for others. A 2024 educational warning noted that cryptocurrency may decline or lose most or all of its value at any time. A user can also lose access to assets by losing passwords or private keys.
Smart Contracts and Decentralized Finance
Smart contracts are programs stored and executed on a blockchain. Their terms are written in code. Instead of transferring only a currency, a user can submit an instruction like "If event X occurs, then execute action Y."
A smart contract may process defined inputs and produce an output - releasing funds, recording ownership, changing a state, or transferring an asset. Ethereum demonstrated how a public blockchain could serve as a distributed computer for conditional agreements.
Smart contracts enabled decentralized finance (DeFi) by providing financial services through programmable applications rather than only through traditional intermediaries. Potential examples include conditional payments, decentralized exchanges, lending or borrowing, asset management, tokenized funds, automated insurance, payment settlement, stablecoins, and prediction markets.
Smart contracts can automate execution and reduce manual processing, but the network executes the contract's code as written. Code behavior and the quality of the underlying data remain important. This relates to crypto currency applications - DeFi is one major category, but not the only one.
Asset Tokenization and NFTs
A blockchain can function as a shared registry for assets. A smart contract can create a token that represents ownership or a defined interest in an asset. Examples include buildings, cars, rare trading cards, digital media, music, concert tickets, contracts, and medical-record references.
Tokenization can provide a shared ownership or provenance record, authenticity checks, a transparent asset history, transferable rights, potentially broader market access, asset lifecycle tracking, and a potential liquidity layer for assets that previously had limited buyers.
A non-fungible token (NFT) is a unique blockchain-based token. NFTs can represent unique digital media such as art, video, or music, and they may also be used in claims tied to physical assets. A unique token can carry information about authenticity, ownership, and history. NFTs may allow creators to sell works and retain a share or attribution through smart contracts.
The sources emphasize that a token can record a right, but the legal interpretation of that right may depend on the agreement surrounding it. Tokenization doesn't cause physical goods to become reproducible. A tokenized building remains a building, while the token and ledger provide information about rights or transfers. If you're looking to create nft for free , you'll still need to pay network fees - the "free" part usually refers to platform fees, not the underlying blockchain cost.
Provenance, Ownership, and Double Selling
Digital goods are abstract and reproducible. Software, music, images, and other files can be copied effortlessly. Because replicas are easy to create, the copies or representations may not carry the same value as the original creation. The integrity of the original digital asset is therefore important.
Hashes and blockchain records can provide evidence that digital content has not changed. In some cases, a token serves as a unique reference to an original file, work, or ownership record. A digital asset can be replicated across many locations, which can increase confidence that it will remain available. That permanence isn't absolute - digital information still depends on physical storage such as hard drives, which can fail, degrade, or become obsolete.
DLT can establish the history of a registered item from replicated ledgers without asking one centralized registry to supply every historical record. Block order and ownership references can help prevent two owners from selling the same recorded asset twice within the same period. A buyer still needs assurance that the asset is genuine, the seller owns it or is authorized to act for the owner, the recorded history is accurate, and the token has not already been transferred or double-spent.
Blockchains can provide a shared provenance record, but the relationship between a physical item and its digital representation must still be established. This is a key limitation - the blockchain records what you tell it, but it can't verify the physical world on its own.
Enterprise Middleware and Shared Records
Blockchains can act as middleware between organizations that don't want to place full confidential records on a public ledger. Each enterprise may retain sensitive internal data while writing a shared event, commitment, or proof to the blockchain.
A zero-knowledge proof can serve as a common reference without disclosing the underlying sensitive content to every participant. For example, two businesses could use a ledger to confirm the current terms of a volume-discount agreement without publishing all of the agreement's confidential data.
Enterprise uses
- Shared business-process state
- Audit trails
- Financial contract tracking
- Medical-record references
- Identity records
- Asset servicing
- Settlement status
- Proof of reserve
- Regulatory compliance
A "ledger of record" is a trusted, immutable historical environment. It can reduce the friction caused by fragmented databases and databases maintained by different institutions. Corrections, deletion, privacy requirements, and governance remain significant design issues.
Identity and Key Recovery
A simple decentralized identity is based on a public key. The public key serves as the identifier, and the private key signs messages. Several identity problems arise: what happens if a key is stolen, what happens if a key is lost, how can a person use a readable name instead of a random cryptographic address, and how can multisignature or more advanced security rules be used.
Distributed hash tables can store key information and provide revocation records, but they don't by themselves solve every temporal problem. If a key is stolen, both the owner and attacker may possess it, making a replacement difficult to establish. Blockchain timestamping can help record when a revocation or key change occurred.
Multisignature systems can require more than one key to authorize an action. In one example, a person selects eight entities - friends, an employer, a corporation, or a nonprofit - and five of them must cooperate to recover a key. This is called social multisignature backup. It provides recovery without relying on one central account administrator.
Secret sharing can divide a key into mathematical shares. If one share is lost, enough remaining shares can reconstruct it. A blockchain-based name registry can point a readable name to a contract or key. On Ethereum, a contract can maintain an identity's current key, backup keys, and update logic. The identity can therefore be programmed to recover from mistakes or key loss without one company controlling every recovery process.
Supply Chains and Product Provenance
As an immutable distributed database, blockchain can improve traceability and coordination among participants in a supply chain. Each participant can hold a copy of the ledger, inspect transaction status, identify errors, and review previous actions.
If a product is recorded as moving through several stages, participants can examine when each transfer occurred and which organization recorded it. One participant cannot overwrite historical data without creating a mismatch with the other shared copies unless it re-writes all later blocks or the network adopts a fork.
Supply chain applications
- Farm-to-table tracking
- Product authenticity
- Pharmaceutical provenance
- Food safety
- Digital product records
- Logistics coordination
- IoT registration
- Machine-to-machine communication
The value depends on the quality of the initial data and on whether participants have incentives to enter accurate information. Garbage in, garbage out still applies.
When a Blockchain May or May Not Be Appropriate
A decision framework compares blockchain with ordinary databases according to the number of writers and the degree of trust required.
If no database is needed, a blockchain cannot add value. If only one actor writes the data, a standard database is generally simpler - most internal enterprise applications fall into this category. If all writers are trusted, a conventional permissioned database may provide the same result without blockchain's added complexity. If a trusted third party can regulate the record, a blockchain may add complexity without a corresponding benefit.
A blockchain is most directly suited to a situation involving many participants that don't fully trust one another, all of which need to write to a shared database. The participants need an auditable history, direct interaction, and a way to agree on changes without relying on one organization's master copy. Examples can include IoT registration, machine-to-machine communication, and some transaction systems.
This framework does not make blockchain automatically superior in a multi-party environment. It asks whether its properties are actually necessary. Public, private, and consortium systems are available, as are open-source and proprietary implementations. Each introduces different language, governance, identity, and deployment requirements.
The system must still have a viable governance model, sufficient participation, meaningful incentives, and a consensus mechanism. Before building such a system, the source material proposes asking: who will participate, why would they maintain it, what's their incentive, what data or service would drive adoption, why should the data network be decentralized rather than centrally managed, how will participants reach consensus, how will inaccurate or disputed data be handled, how will upgrades and forks be governed, how will participants be compensated for validation and storage, can the system reach enough scale to resist manipulation, and is the expected benefit greater than the computational, financial, and organizational cost.
The Long Tail of Blockchain Applications
Vitalik Buterin's 2015 analysis argued that there would be no single "killer app" for blockchain. If one application had been overwhelmingly superior for a major part of society's infrastructure, people would already be pursuing it. By 2015, many people with substantial financial incentive had searched the market, but no single application had emerged as dominant.
The closest early examples were censorship-resistant payment and donation systems. Silk Road, an anonymous online drug marketplace shut down by law enforcement in late 2013, processed more than $1 billion in sales during its 2.5 years of operation. During a payment blockade against WikiLeaks, Bitcoin and Litecoin donations represented the bulk of WikiLeaks's revenue. These systems met a clear need and allowed users to bypass a conventional restriction.
Those cases achieved high utility for a narrow group. They didn't show that blockchain was indispensable to everyone. The broader opportunity was described as a long tail of applications in which blockchain may be marginally better than the next available tool rather than absolutely necessary.
Open source software offers a similar pattern - it has benefited society and is used in millions of software packages, yet it doesn't have one universal application. Its value is distributed across lower-level libraries and tools that are repeatedly reused.
"A blockchain is a magic computer that anyone can upload programs to and leave the programs to self-execute, where the current and all previous states of every program are always publicly visible, and which carries a very strong cryptoeconomically secured guarantee that programs running on the chain will continue to execute in exactly the way that the blockchain protocol specifies."
This definition emphasizes a shared computer and persistent program state rather than money or one specific transaction type. It doesn't require a particular consensus algorithm, financial currency, or state-transition rule. Cryptoeconomic security combines public-key authentication, decentralization, economic incentives, and resistance to reversing history.
The underlying value was described as creating economic and social institutions with rules that can be deployed and changed under community control. The applications can communicate, reuse shared data, and remain available even when individual operators lose interest or change incentives.
Benefits Attributed to Blockchain
In a sufficiently decentralized blockchain, malicious actors would have to overcome many independently maintained copies to change the accepted ledger. Cryptographic links make modifications detectable, and consensus rules make it difficult for one participant to rewrite history alone.
Once a block is redundantly confirmed, changing it would normally require changing every later block and convincing the network to accept the alternative. The cost of alteration generally increases as additional blocks are added.
Participants can inspect the transactions and rules on a public ledger. Historical activity can be audited without relying entirely on an opaque internal database. Transparency can increase trust when users can verify what was recorded, although public visibility doesn't automatically mean that every participant's real-world identity is known.
Globally distributed networks can remain online 24 hours a day and are not restricted to one geographic location or political jurisdiction. A sufficiently redundant network can continue operating even when individual computers fail.
Parties can transact directly rather than routing every transfer through an intermediary. The intended benefits can include fewer reconciliations, fewer administrative steps, and reduced dependence on one intermediary's willingness or ability to settle.
Computational validation can reduce human error in transaction processing. Nodes apply the same rules rather than independently entering each transaction into separate databases. Invalid signatures, insufficient balances, or malformed transactions can be rejected.
Limitations, Risks, and Trade-Offs
PoW mining requires specialized hardware, electricity, and trial-and-error computation. In Bitcoin's PoW model, many participants compete, and only one ultimately produces the accepted block. The energy used by the network is therefore an important cost. A 2018 estimate put Bitcoin energy consumption at 62.24 terawatt-hours - described as enough to power Switzerland. This was a historical estimate and shouldn't be read as a current measurement. Energy use varies with network rules, hardware, participation, and the price of electricity.
PoS is designed to reduce the computational work associated with mining, although it has a different governance and security model. Not every blockchain uses PoW. Permissioned systems using proof of authority or other consensus mechanisms may consume much less energy because they operate with a restricted validator set. That reduction in computation comes with a different degree of openness and decentralization.
A blockchain can process transactions while traditional institutions are closed, but that doesn't mean every transaction is immediate. Transactions may wait for a block, and blocks may be produced at fixed intervals. Confirmation can take seconds, minutes, or longer depending on the network and its congestion.
A chain has limited block capacity and an expanding data history. Storing large files or high volumes of data directly can be expensive or impractical. Some applications therefore place references or proofs on-chain while keeping larger data elsewhere.
Every full participant that maintains the entire ledger must store and process duplicated data. Replication provides resilience, but it also consumes storage, bandwidth, and computing resources.
Once a transaction is confirmed, it's generally difficult to reverse. A mistaken transfer may not have the same revocation mechanism available through a bank or payment processor. A user must therefore check addresses, keys, amounts, and transaction details carefully.
A public ledger can expose addresses, balances, transaction timing, and amounts. Pseudonymous addresses don't automatically conceal the people controlling them. Privacy can be enhanced through careful design, zero-knowledge proofs, encryption, or permissioned access, but these mechanisms have different guarantees.
Storing personal or medical information directly on an immutable public ledger can conflict with the need to correct, restrict, or delete that information. One proposed enterprise pattern is to keep sensitive records off-chain and place a transaction, hash, or zero-knowledge proof on the shared ledger.
A network may be described as decentralized while a small number of validators, mining pools, software developers, cloud providers, or governance participants hold substantial control. A permissioned blockchain depends on known administrators and participating organizations. A public blockchain depends on the distribution of hashing power, stake, governance influence, and node ownership.
Participants may disagree about protocol rules, upgrades, forks, validation rules, or disputed transactions. A network needs enough active, independent participants to make manipulation expensive. A small network cannot provide the same resistance as a large, distributed one.
Blockchains can reliably enforce the rules supplied to them, but they cannot independently establish that a real-world statement entered into a transaction is true. An incorrect price, identity claim, product attribute, or event description can be permanently recorded if the protocol accepts it.
Cryptocurrencies have historically been used in illegal activity. Pseudonymity and difficult reversibility can complicate tracing and enforcement. Regulatory systems also have difficulty classifying blockchain-based assets - questions include who holds custody, how ownership is recognized, how tax is applied, how consumer protection works, and whether a token represents a currency, commodity, security, property interest, or another contractual right.
Building a blockchain application requires more than adding a database. Participants need a governance model, validator rules, incentives, node software, key management, upgrade procedures, and a way to handle disputes. For many applications, a conventional database is cheaper and simpler. This connects to how does crypto currency works - the answer involves understanding these trade-offs, not just the happy path.
Design Choices and the Scalability Trilemma
Blockchain designs vary in network access and participation, consensus, privacy, finality, scalability, and governance. The three main access patterns are public, private, and permissioned. Consensus can be reached through PoW, PoS, PoA, or other rules. No single mechanism provides the same combination of openness, performance, governance, and resource use.
A design commonly faces the blockchain scalability trilemma - a trade-off among security, decentralization, and scalability. A blockchain cannot maximize all three at once under every design. Other important features include privacy, transaction finality, programmability, throughput, latency, storage requirements, regulatory accessibility, and administrative control.
A system optimized for many users and high transaction volume may use greater centralization or a different consensus design. A system optimized for privacy may restrict access. A system optimized for rapid finality may rely on a smaller validator set. A PoW system may favor open participation while using substantial computation and energy. A permissioned system may lower computational cost while placing more trust in its administrators and member organizations.
Trust in Software, Rules, and Governance
A blockchain changes where trust is placed. Traditional financial transactions often depend on a trusted intermediary such as a bank, payment processor, clearinghouse, or government registry. A blockchain attempts to replace or reduce that single point of trust with replicated records, cryptographic authentication, deterministic software, public or auditable validation rules, consensus among validators, economic incentives, and governance procedures.
The claim that blockchain removes trust is too broad. It redistributes trust. Users must trust or verify the software, the consensus rules, the validators, the governance process, and the incentives that keep them participating. A network can reduce reliance on probabilistic trusted third parties, but it cannot guarantee that code, entered data, or governance decisions are correct.
A smart contract executes the instructions it was given; the question is whether those instructions represent the intended agreement. A validator network can agree on a record without proving that an off-chain event was described accurately. This is why what is the crypto currency matters less than understanding the full stack - the token is one piece, but the rules, governance, and incentives are what make the system work or fail.
Base-Layer Infrastructure
The largest gains were expected to come from base-layer infrastructure services with three properties: dependency (many other services rely directly on the base service), network effects (more users make the service more valuable), and switching costs (users may find it difficult to move to another service).
Language, roads, legal systems, postal networks, transportation systems, telephone networks, financial systems, and the internet are examples of base-layer infrastructure. Newer informational services include internet payment systems, identity, domain-name systems, certificate authorities, reputation systems, cloud computing, data feeds, and prediction markets.
If many services become interconnected, a failure or controversial governance decision at one of these layers may affect large numbers of downstream applications. The 2015 discussion used certificate authorities as an example - attackers obtained nine fraudulent SSL certificates through a compromised reseller. The discussion asked why certificate authorities couldn't operate in a more decentralized M-of-N structure in which several independent authorities had to authorize a change. A blockchain can provide shared infrastructure for coordinating such rules.
Decentralized Identity and Reputation in the Long Tail
The identity section of the long-tail model asks how a person can recover a stolen or lost key, use a readable name, or move to a stronger multisignature system. A public key can serve as an identity, and signatures prove control of that key. A hash-based name system can provide a shorter readable identifier. A distributed hash table can store the actual public key, while a blockchain records revisions and key history.
If a key is stolen, the owner and attacker may both present valid signatures. Revocation alone doesn't establish which history is authoritative. A blockchain can provide a timestamped record of the legitimate key replacement. A three-key arrangement could require two or three existing keys to approve a new key. However, if an attacker obtains every old key from an earlier point, the attacker may be able to simulate a competing key history. Timestamping through a blockchain is intended to make such a rewrite harder.
Blockchain-based name registries can map names to contracts or keys. On Ethereum, a contract can maintain an identity's active key and backup keys. A user may be able to recover a key through a social M-of-N system without relying on one institution.
Reputation systems can use the same shared state. Ratings could be tied to blockchain payments, so a user might be able to prove that an interaction occurred before submitting a rating. A reputation algorithm could then calculate a score from shared records. A zero-knowledge proof could reveal that a person meets a threshold without disclosing every underlying rating.
The long-tail argument doesn't claim that centralized services are useless. It argues that decentralized alternatives may be preferable when users want open access, portability, cryptographic verification, and less dependence on a single platform.
Consensus as an Incentive Problem
A shared ledger needs participants to communicate, validate transactions, store data, and maintain the network. If there's no reward or reason to participate, the system may fail to attract enough contributors.
PoW compensates the successful validator and makes malicious participation costly. A validation process that required no work could be manipulated by a group of colluding nodes without spending enough resources to outweigh their reward. In permissioned networks, incentives may be contractual, reputational, or administrative rather than monetary. A company may operate a validator because it benefits from shared settlement or because it has signed a participation agreement.
Critical mass is significant. A blockchain with very few validators can still work if its participants know and trust one another, but that's closer to a permissioned database network than to a high-decentrality public chain. The security claims must specify whether they rely on cryptography, governance, or trusted organizations.
Comments on “What Is Blockchain Tech? How Blocks and Ledgers Help Build Trust”
No comments yet. Be the first to share your thoughts.